


 Home

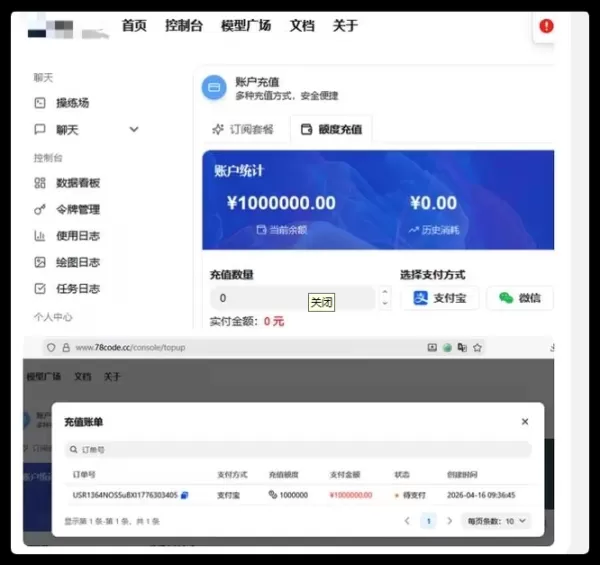
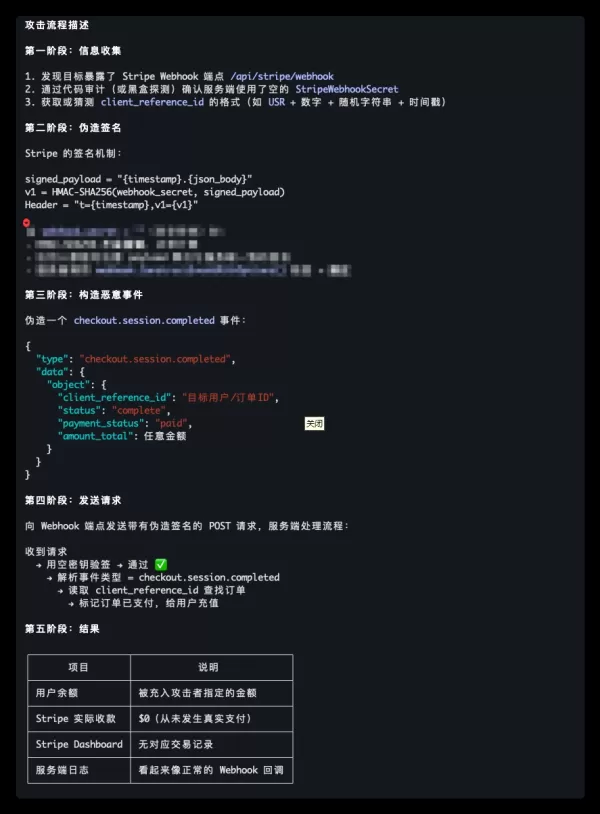
A critical vulnerability has been identified in the AI model management system QuantumNous/new-api (NewAPI). When the Stripe payment key is left unconfigured, attackers can forge webhook events to bypass payment, enabling "zero-cost" arbitrary account top-ups. The flaw stems from inadequate signature verification for empty keys during payment callbacks. The project has released a patched version (v0.12.10). All users are urged to upgrade immediately, configure a strong Stripe Secret Key, and audit their recharge records.
Comments (0)
0/300






