


 Home
Microsoft Copilot Vulnerable to Indirect Prompt Injection, Hidden Report Reveals
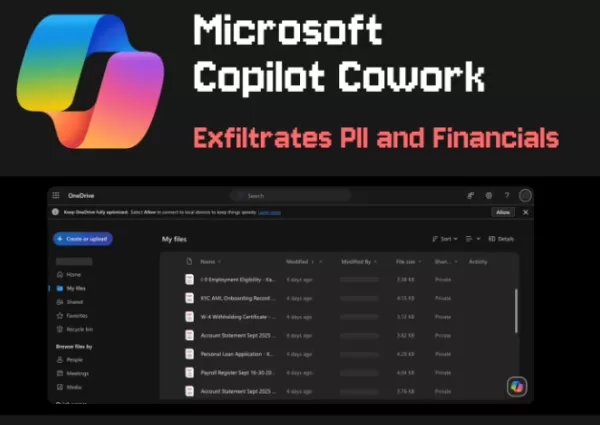
Safety research firm PromptArmor recently published a report highlighting a serious security flaw in Microsoft's AI agent service Copilot Cowork, which is part of Microsoft 365. Attackers can use a method known as "indirect prompt injection" to quietly steal and leak confidential files from an organization's internal cloud storage without user consent.
Malicious Instructions Concealed in Office Templates
As an integrated AI assistant, Cowork has broad permissions to send emails, post messages in Teams, and access internal data from OneDrive and SharePoint. However, researchers have discovered that attackers can embed harmful instructions within web pages, documents, or seemingly routine office automation templates, such as a "Weekly Work Review," to trick the AI agent into executing them.
When a user asks Cowork to handle a file that contains these malicious prompts, the AI agent is deceived into falsely claiming it needs to generate a document preview. Then it automatically retrieves pre-authenticated download links for sensitive files and sends those links back to the attacker through Teams messages—all carried out in the background, making it extremely hard for users to notice.
Scheduled Tasks Amplify Risk and Are Hard to Block
The report notes that because Copilot Cowork can perform tasks on a scheduled basis, this significantly increases the security danger. For instance, recurring automated tasks like "Weekly Report Summary," which run periodically, can repeatedly trigger and execute the attack chain in the background—even when the user is away from their screen and not actively using the system.
In security tests, this attack method achieved a 100% success rate across five trials. Worse still, administrators have limited ability to monitor or control such "skill files," and the vulnerability is not only effective in automatic mode but also remains exploitable when explicitly calling more powerful large models like Claude Opus 4.7.
Related article
 Stripe to Acquire OpenRouter as AI Model Routing Gains Momentum
Stripe has agreed to acquire OpenRouter, an AI model-routing platform that gives developers access to hundreds of models through a single interface. The deal adds model selection and routing to Stripe’s existing work around AI usage and token-based b
Former OpenAI Researcher Barrett Zoph Returns to Google to Support Gemini Development
Barret Zoph, who previously abruptly left and joined OpenAI due to a disagreement with Thinking Machines Lab CEO Miriam Mularati, has once again changed employers. Alphabet's Google announced that Zoph will return as Vice President of Research, bring
How Recursive Intelligence Raised $335M at $4B Valuation in 4 Months
The co-founders of startup Ricursive Intelligence seemed destined to be co-founders.Anna Goldie, CEO, and Azalia Mirhoseini, CTO, are so well-known in the AI community that they were among those AI engineers who “got those weird emails from Zuckerber
Related Special Topic Recommendations
Design & Art
 Top AI Illustration Tools: Create Editorial Scenes and Cover Art Faster
2026 Latest Top-rated AI Illustration Tools: Our curated list features the best powerfully designed tools for creating stunning editorial scenes and eye-catching cover art quickly. Each option has gone through rigorous real-world tests, offering a free vs paid comparison to help you find the perfect match for your workflow. Try these must-try solutions today to unlock your AI edge and boost your creative productivity. Explore now at XIX.AI.
 10 tools
 xix.ai
Education and Learning
Top AI Tutors for Exam Prep: Practice Math, Science, and English
2026 Latest Top-Rated Best AI Tutors for Exam Prep are here on XIX.AI! Our curated list features powerful game-changing tools that offer free vs paid comparison, real-world tests, and weekly updated rankings. They help boost your writing efficiency, simplify complex topic learning, and unlock your academic potential. Explore now to Discover your perfect exam prep tool and Start creating today to Unlock your AI edge!
10 tools
xix.ai
Finance
AI Budget Planning Tools for Personal Money Management
2026 Latest Best Top-Rated AI Budget Planning Tools for Personal Money Management are here on XIX.AI! This curated collection features powerful, game-changing solutions that help you conduct real-world tests, understand spending habits, and create personalized plans to boost productivity. Enjoy a free vs paid comparison along with detailed rankings. Must-try tools designed to simplify money management and unlock your AI edge. Explore now!
11 tools
xix.ai
Health & Wellness
AI Sleep Tracking Assistants: Improve Recovery with Better Bedtime Habits
2026 Latest Best Top-Rated AI Sleep Tracking Assistants curated for ultimate recovery. This fully updated weekly guide features powerful tools that deliver real-world tests, free vs paid comparison, and detailed rankings to help you find the must-try solution that boosts sleep quality and supports better bedtime habits. Explore now at XIX.AI to Unlock your AI edge.
10 tools
xix.ai
Data Analysis
AI SQL Copilots for Product and Revenue Analytics
2026 Latest Best Top-Rated AI SQL Copilots for Product and Revenue Analytics! XIX.AI has curated a powerful, game-changing collection of must-try tools that undergo real-world tests through weekly updated rankings. These tools help users boost productivity significantly by accelerating data analysis, streamlining complex queries, and generating accurate insights to drive smarter business decisions. Explore now to Discover your perfect tool for unlocking your AI edge!
14 tools
xix.ai
Education and Learning
Best AI Homework Helpers That Teach: Learn Concepts, Not Just Answers
2026 Latest Best Top-Rated AI Homework Helpers That Teach Core Concepts Not Just Answers Powerful Tools for Students Must-Try Curated List Weekly Updated Free vs Paid Comparison Real-World Tests Accurate Rankings to Help You Unlock Your Full Learning Potential Explore now to Discover your perfect tool for smarter studying.
10 tools
xix.ai

 Comments (0)
0/500
Safety research firm PromptArmor recently published a report highlighting a serious security flaw in Microsoft's AI agent service Copilot Cowork, which is part of Microsoft 365. Attackers can use a method known as "indirect prompt injection" to quietly steal and leak confidential files from an organization's internal cloud storage without user consent.
Malicious Instructions Concealed in Office Templates
As an integrated AI assistant, Cowork has broad permissions to send emails, post messages in Teams, and access internal data from OneDrive and SharePoint. However, researchers have discovered that attackers can embed harmful instructions within web pages, documents, or seemingly routine office automation templates, such as a "Weekly Work Review," to trick the AI agent into executing them.
When a user asks Cowork to handle a file that contains these malicious prompts, the AI agent is deceived into falsely claiming it needs to generate a document preview. Then it automatically retrieves pre-authenticated download links for sensitive files and sends those links back to the attacker through Teams messages—all carried out in the background, making it extremely hard for users to notice.
Scheduled Tasks Amplify Risk and Are Hard to Block
The report notes that because Copilot Cowork can perform tasks on a scheduled basis, this significantly increases the security danger. For instance, recurring automated tasks like "Weekly Report Summary," which run periodically, can repeatedly trigger and execute the attack chain in the background—even when the user is away from their screen and not actively using the system.
In security tests, this attack method achieved a 100% success rate across five trials. Worse still, administrators have limited ability to monitor or control such "skill files," and the vulnerability is not only effective in automatic mode but also remains exploitable when explicitly calling more powerful large models like Claude Opus 4.7.








 Stripe to Acquire OpenRouter as AI Model Routing Gains Momentum
Stripe has agreed to acquire OpenRouter, an AI model-routing platform that gives developers access to hundreds of models through a single interface. The deal adds model selection and routing to Stripe’s existing work around AI usage and token-based b
 Former OpenAI Researcher Barrett Zoph Returns to Google to Support Gemini Development
Barret Zoph, who previously abruptly left and joined OpenAI due to a disagreement with Thinking Machines Lab CEO Miriam Mularati, has once again changed employers. Alphabet's Google announced that Zoph will return as Vice President of Research, bring
 How Recursive Intelligence Raised $335M at $4B Valuation in 4 Months
The co-founders of startup Ricursive Intelligence seemed destined to be co-founders.Anna Goldie, CEO, and Azalia Mirhoseini, CTO, are so well-known in the AI community that they were among those AI engineers who “got those weird emails from Zuckerber

2026 Latest Top-rated AI Illustration Tools: Our curated list features the best powerfully designed tools for creating stunning editorial scenes and eye-catching cover art quickly. Each option has gone through rigorous real-world tests, offering a free vs paid comparison to help you find the perfect match for your workflow. Try these must-try solutions today to unlock your AI edge and boost your creative productivity. Explore now at XIX.AI.
10 tools
xix.ai

2026 Latest Top-Rated Best AI Tutors for Exam Prep are here on XIX.AI! Our curated list features powerful game-changing tools that offer free vs paid comparison, real-world tests, and weekly updated rankings. They help boost your writing efficiency, simplify complex topic learning, and unlock your academic potential. Explore now to Discover your perfect exam prep tool and Start creating today to Unlock your AI edge!
10 tools
xix.ai

2026 Latest Best Top-Rated AI Budget Planning Tools for Personal Money Management are here on XIX.AI! This curated collection features powerful, game-changing solutions that help you conduct real-world tests, understand spending habits, and create personalized plans to boost productivity. Enjoy a free vs paid comparison along with detailed rankings. Must-try tools designed to simplify money management and unlock your AI edge. Explore now!
11 tools
xix.ai

2026 Latest Best Top-Rated AI Sleep Tracking Assistants curated for ultimate recovery. This fully updated weekly guide features powerful tools that deliver real-world tests, free vs paid comparison, and detailed rankings to help you find the must-try solution that boosts sleep quality and supports better bedtime habits. Explore now at XIX.AI to Unlock your AI edge.
10 tools
xix.ai

2026 Latest Best Top-Rated AI SQL Copilots for Product and Revenue Analytics! XIX.AI has curated a powerful, game-changing collection of must-try tools that undergo real-world tests through weekly updated rankings. These tools help users boost productivity significantly by accelerating data analysis, streamlining complex queries, and generating accurate insights to drive smarter business decisions. Explore now to Discover your perfect tool for unlocking your AI edge!
14 tools
xix.ai

2026 Latest Best Top-Rated AI Homework Helpers That Teach Core Concepts Not Just Answers Powerful Tools for Students Must-Try Curated List Weekly Updated Free vs Paid Comparison Real-World Tests Accurate Rankings to Help You Unlock Your Full Learning Potential Explore now to Discover your perfect tool for smarter studying.
10 tools
xix.ai












