


 Home
OpenAI Enhances Codex Security with Dangerous Operation Blocking and Permission Controls
OpenAI has bolstered the security framework for its AI coding agent, Codex, by introducing multiple safeguards designed to mitigate risks associated with destructive actions, such as accidental file deletion or data overwriting during code execution.
According to a recent post by OpenAI team member Tibo, the company investigated reports of harmful operations originating from Codex and identified that the primary vulnerabilities occurred during the cleanup of temporary working directories. Key issues included the improper reuse of system variables, such as $HOME, which could inadvertently direct cleanup processes to actual user directories. Furthermore, certain operations lacked adequate path verification prior to deletion or overwriting, thereby increasing the potential for data corruption.
To resolve these vulnerabilities, OpenAI has implemented multi-layered protections. The updated Codex version now requires agents to validate target paths before executing sensitive operations and utilizes isolated temporary directories, eliminating reliance on potentially misleading system variables. Additionally, OpenAI has enhanced its mechanisms for identifying and blocking dangerous commands, while introducing supplementary review procedures for these operations.
Moreover, OpenAI has increased the requirements for granting Codex Full access permissions. By incorporating more prominent risk warnings, the company aims to reduce the likelihood of users inadvertently authorizing broad access. These upgrades to Auto-review rules further restrict security risks without compromising the efficiency of AI-assisted programming.
As AI coding agents become increasingly integrated into code development, file management, and automated task execution, ensuring the safety of agent behavior has emerged as a critical industry priority. This enhancement by OpenAI underscores the necessity for AI Agents to continuously refine their permission management, operational auditing, and risk control capabilities as their application scope expands.
Related article
 WeChat Pay launches Smart Glasses SDK; Rokid becomes first compatible brand
WeChat has officially launched the WeChat Pay smart glasses SDK, making it fully accessible. This solution integrates WeChat’s core “scan to pay” functionality into a standard SDK, available to smart glasses manufacturers meeting specific standards.
Uber Engineer Creates AI Clone of CEO to Dodge Direct Questions
While most staff dread reporting to the CEO, engineers at global travel leader Uber have discovered a strategic advantage: letting an AI replica of their boss provide feedback beforehand."Dara AI": The Executive Coach Before Boardroom MeetingsUber CE
How Unitree is Shaping the Future of Humanoid Robotics
Unitree’s New Creature of Embodied AI with ultra-wide 4D LiDAR technology for advanced real-world navigation. Credit: UnitreeWang Xingxing, CEO of Unitree, targets world model breakthroughs to help humanoid machines execute 80% of tasks when placed i
Related Special Topic Recommendations
Health & Wellness
 Best AI Sleep Coaching Tools for Shift Workers, Jet Lag Recovery, and Better Routines
2026 Latest Best AI Sleep Coaching Tools for Shift Workers, Jet Lag Recovery, and Better Routines! XIX.AI has curated a top-rated list of powerful game-changing tools that go through real-world tests to deliver accurate guidance. You can find detailed free vs paid comparison info and see how these must-try solutions help boost sleep quality, speed up jet lag recovery, and build healthier routines. Explore now to discover your perfect tool!
 7 tools
 xix.ai
code
ChatGPT Debugging Tools for Python Errors, API Logs, and Stack Trace Triage
2026 Latest Best ChatGPT debugging tools for Python errors, API logs, and stack trace triage are here on XIX.AI. This curated list of top-rated solutions offers a free vs paid comparison, real-world tests, and detailed rankings to help you find the most powerful tool that can significantly boost your productivity and help you solve complex technical issues faster. Explore now to discover your perfect solution!
9 tools
xix.ai
Text-to-speech
AI Voiceover Tools for Product Demo Videos
2026 Latest Best Top-Rated AI Voiceover Tools for Product Demo Videos are here on XIX.AI! This curated list features powerful, game-changing options that help you create professional-quality audio content fast, boosting your demo efficiency significantly. We conduct real-world tests and provide a free vs paid comparison along with weekly updated rankings to help you find the perfect fit. Explore now to Unlock your AI edge!
10 tools
xix.ai
Business
AI Business Plan Tools for Startup Validation
2026 Latest Best AI Business Plan Tools for Startup Validation! XIX.AI has curated a top-rated list of powerful game-changing tools that go through real-world tests to deliver accurate results. You’ll find a free vs paid comparison, detailed rankings, and easy-to-understand insights to help you choose the perfect solution and boost your startup’s success rate. Explore now to Unlock your AI edge!
9 tools
xix.ai
chatbot
AI Chat Apps for Roleplay and Conversation Practice
2026 Latest Best AI Chat Apps for Roleplay and Conversation Practice! XIX.AI curates a top-rated list of powerful must-try tools that go through rigorous real-world tests to deliver exceptional results. You’ll find detailed free vs paid comparison, comprehensive rankings, and insights into how these apps can boost your language skills and communication confidence effectively. Explore now to discover your perfect tool for practice!
10 tools
xix.ai
design
Best AI Wireframe Tools for Product Teams
2026 Latest Best Top-rated AI Wireframe Tools for Product Teams! This curated list showcases powerful, game-changing solutions that significantly boost productivity through real-world tests and rigorous rankings. It includes a detailed free vs paid comparison to help you find the perfect fit. XIX.AI provides expert insights to guide your decision. Explore now to Discover your perfect tool and Unlock your AI edge in product development!
8 tools
xix.ai

 Comments (0)
0/500
OpenAI has bolstered the security framework for its AI coding agent, Codex, by introducing multiple safeguards designed to mitigate risks associated with destructive actions, such as accidental file deletion or data overwriting during code execution.
According to a recent post by OpenAI team member Tibo, the company investigated reports of harmful operations originating from Codex and identified that the primary vulnerabilities occurred during the cleanup of temporary working directories. Key issues included the improper reuse of system variables, such as $HOME, which could inadvertently direct cleanup processes to actual user directories. Furthermore, certain operations lacked adequate path verification prior to deletion or overwriting, thereby increasing the potential for data corruption.
To resolve these vulnerabilities, OpenAI has implemented multi-layered protections. The updated Codex version now requires agents to validate target paths before executing sensitive operations and utilizes isolated temporary directories, eliminating reliance on potentially misleading system variables. Additionally, OpenAI has enhanced its mechanisms for identifying and blocking dangerous commands, while introducing supplementary review procedures for these operations.
Moreover, OpenAI has increased the requirements for granting Codex Full access permissions. By incorporating more prominent risk warnings, the company aims to reduce the likelihood of users inadvertently authorizing broad access. These upgrades to Auto-review rules further restrict security risks without compromising the efficiency of AI-assisted programming.
As AI coding agents become increasingly integrated into code development, file management, and automated task execution, ensuring the safety of agent behavior has emerged as a critical industry priority. This enhancement by OpenAI underscores the necessity for AI Agents to continuously refine their permission management, operational auditing, and risk control capabilities as their application scope expands.








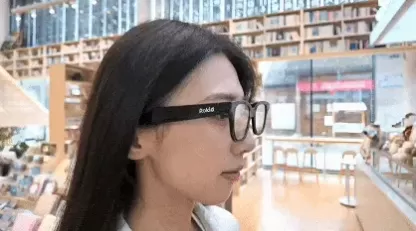 WeChat Pay launches Smart Glasses SDK; Rokid becomes first compatible brand
WeChat has officially launched the WeChat Pay smart glasses SDK, making it fully accessible. This solution integrates WeChat’s core “scan to pay” functionality into a standard SDK, available to smart glasses manufacturers meeting specific standards.
 Uber Engineer Creates AI Clone of CEO to Dodge Direct Questions
While most staff dread reporting to the CEO, engineers at global travel leader Uber have discovered a strategic advantage: letting an AI replica of their boss provide feedback beforehand."Dara AI": The Executive Coach Before Boardroom MeetingsUber CE
 How Unitree is Shaping the Future of Humanoid Robotics
Unitree’s New Creature of Embodied AI with ultra-wide 4D LiDAR technology for advanced real-world navigation. Credit: UnitreeWang Xingxing, CEO of Unitree, targets world model breakthroughs to help humanoid machines execute 80% of tasks when placed i

2026 Latest Best AI Sleep Coaching Tools for Shift Workers, Jet Lag Recovery, and Better Routines! XIX.AI has curated a top-rated list of powerful game-changing tools that go through real-world tests to deliver accurate guidance. You can find detailed free vs paid comparison info and see how these must-try solutions help boost sleep quality, speed up jet lag recovery, and build healthier routines. Explore now to discover your perfect tool!
7 tools
xix.ai
2026 Latest Best ChatGPT debugging tools for Python errors, API logs, and stack trace triage are here on XIX.AI. This curated list of top-rated solutions offers a free vs paid comparison, real-world tests, and detailed rankings to help you find the most powerful tool that can significantly boost your productivity and help you solve complex technical issues faster. Explore now to discover your perfect solution!
9 tools
xix.ai
2026 Latest Best Top-Rated AI Voiceover Tools for Product Demo Videos are here on XIX.AI! This curated list features powerful, game-changing options that help you create professional-quality audio content fast, boosting your demo efficiency significantly. We conduct real-world tests and provide a free vs paid comparison along with weekly updated rankings to help you find the perfect fit. Explore now to Unlock your AI edge!
10 tools
xix.ai

2026 Latest Best AI Business Plan Tools for Startup Validation! XIX.AI has curated a top-rated list of powerful game-changing tools that go through real-world tests to deliver accurate results. You’ll find a free vs paid comparison, detailed rankings, and easy-to-understand insights to help you choose the perfect solution and boost your startup’s success rate. Explore now to Unlock your AI edge!
9 tools
xix.ai

2026 Latest Best AI Chat Apps for Roleplay and Conversation Practice! XIX.AI curates a top-rated list of powerful must-try tools that go through rigorous real-world tests to deliver exceptional results. You’ll find detailed free vs paid comparison, comprehensive rankings, and insights into how these apps can boost your language skills and communication confidence effectively. Explore now to discover your perfect tool for practice!
10 tools
xix.ai

2026 Latest Best Top-rated AI Wireframe Tools for Product Teams! This curated list showcases powerful, game-changing solutions that significantly boost productivity through real-world tests and rigorous rankings. It includes a detailed free vs paid comparison to help you find the perfect fit. XIX.AI provides expert insights to guide your decision. Explore now to Discover your perfect tool and Unlock your AI edge in product development!
8 tools
xix.ai












