


 Home
Global Websites at Risk as AI Uncovers Critical NGINX Vulnerability
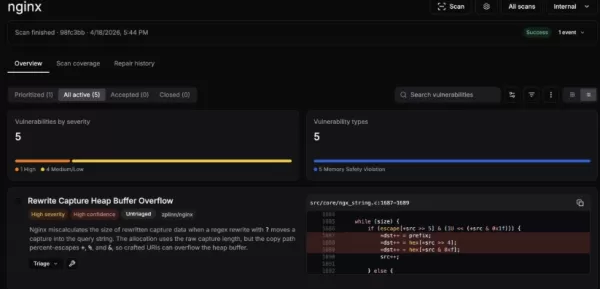
Artificial intelligence has achieved a landmark breakthrough in cybersecurity. The AI-powered security analysis system developed by the startup depthfirst autonomously uncovered a critical vulnerability in NGINX that had remained hidden for 18 yearsCVE-2026-42945 . This flaw, rated Critical (CVSS 9.2), impacts nearly one-third of websites globally, enabling attackers to perform remote code execution (RCE).
Key Vulnerability Details
Exposure Period: The vulnerability went undetected since its introduction in 2008, a span of 18 years.
Affected Versions: NGINX versions from 0.6.27 to 1.30.0.
Vulnerability Mechanism: The flaw resides in the rewrite module, stemming from a defect in the script engine's two-phase processing mechanism, which leads to a heap buffer overflow.
Patched Version: An official patch has been released. It is recommended to upgrade to the open-source version 1.31.0 or 1.30.1, or the corresponding commercial NGINX Plus release.
The Power of AI-Powered Security Analysis
This vulnerability was discovered by the San Francisco-based AI lab depthfirst. The system's capabilities have drawn significant industry attention:
High Efficiency: During just 6 hours of autonomous scanning, the system identified five security issues, including CVE-2026-42945 (four of which have been officially confirmed as remote memory corruption vulnerabilities).
Deep Comprehension: Unlike traditional tools, this AI understands complex business logic and cross-module interactions, uncovering vulnerabilities that even leading AI security tools had missed.
Data indicates approximately 19 million exposed NGINX instances are vulnerable. The United States (roughly 53.4 million affected instances, including historical data) and China (about 25.4 million) show the highest exposure levels. With the proof-of-concept (PoC) code now public, the security risk is severe. All enterprises and developers using NGINX are urged to immediately review their configuration files (particularly in scenarios using both rewrite and set directives) and complete version updates as soon as possible.
Related article
 DeepMind CEO Hassabis: I sleep six hours a day, usually feel energetic around 1 a.m.
Fortune recently featured an interview with Demis Hassabis, CEO of Google DeepMind, revealing his unconventional approach to rest and productivity. Hassabis disclosed that he sleeps very little, structuring his waking hours into two distinct work blo
OpenAI, Anthropic Vie for Market Share Despite Revenue Shortfalls
Despite recent reports suggesting OpenAI missed revenue targets, creating pressure on tech stocks this Tuesday, private AI lab investors remain resilient. Seasoned backers have confirmed they will not reduce investment despite negative media coverage
California AV Compliance: A New Era of Tickets, Geofences, and 1M Miles
Guident operates an AuveTech shuttle in South Florida, managing a four-mile route in West Palm Beach and a one-mile route in Boca Raton using its remote monitoring technology. | Credit: GuidentCalifornia is redefining the regulatory landscape for dri
Related Special Topic Recommendations
chatbot
 Best AI Roleplay Chat Apps for Language Practice, Interview Prep, and Daily Fluency
2026 Latest Best Top-rated AI Roleplay Chat Apps for Language Practice, Interview Prep, and Daily Fluency! XIX.AI curates a powerful game-changing collection that offers free vs paid comparison, real-world tests, and updated rankings weekly. These must-try tools help you boost writing skills, overcome fluency challenges, and improve communication efficiency across all daily scenarios. Explore now to discover your perfect tool for language growth!
 10 tools
 xix.ai
Music composition
AI Stem Separation Tools for Remix Production, Sampling Prep, and Karaoke Masters
2026 Latest Best Top-rated AI Stem Separation Tools Curated for Remix Production, Sampling Prep, and Karaoke Masters. These powerful game-changing tools offer real-world tests to deliver precise audio isolation, boosting productivity significantly. XIX.AI provides a weekly updated free vs paid comparison guide to help you find the must-try solution that suits your needs. Explore now to unlock your AI edge.
8 tools
xix.ai
Data Analysis
AI SQL Copilots for Revenue Dashboards, Funnel Analysis, and Product Metrics
2026 Latest Best AI SQL Copilots Ranked Top-Rated! XIX.AI curates a powerful game-changing collection for weekly updated real-world tests. These must-try tools help you generate accurate revenue dashboards, analyze sales funnels, and track product metrics swiftly, boosting productivity massively. Explore now to Discover your perfect tool for data-driven decision making! 238 characters
9 tools
xix.ai
Music composition
Best AI Melody Writing Tools for Song Drafts
2026 Latest Best Top-Rated AI Melody Writing Tools for Song Drafts! XIX.AI has curated a highly powerful game-changing collection that goes through rigorous real-world tests to deliver the best writing experience. You can find detailed free vs paid comparisons, accurate rankings, and must-try options designed to help you create stunning song drafts effortlessly and boost your creative productivity significantly. Explore now to discover your perfect tool!
8 tools
xix.ai
chatbot
Best AI Conversation Trainer Tools for Interview Practice
2026 Latest Best Top-rated AI Conversation Trainer Tools for Interview Practice are here on XIX.AI! This curated collection features powerful, game-changing tools that go through rigorous real-world tests to deliver accurate feedback. You’ll find a free vs paid comparison and detailed rankings to help you choose the must-try option that boosts your confidence and skills. Explore now to Discover your perfect tool for interview success!
12 tools
xix.ai
Design & Art
Best AI Style Transfer Tools for Creative Experiments
2026 Latest Best Top-rated AI Style Transfer Tools for Creative Experiments! XIX.AI has curated a powerful, game-changing collection of must-try tools that deliver exceptional results through real-world tests and rigorous rankings. These top solutions help creatives boost productivity significantly by accelerating content creation and unlocking endless creative possibilities. Explore now to discover your perfect tool and start creating today!
9 tools
xix.ai

 Comments (1)
0/500
![DanielMartin]()
This is wild. An AI finding a bug that hid for 18 years? Makes you wonder what else is lurking in the code we trust. 😬
Artificial intelligence has achieved a landmark breakthrough in cybersecurity. The AI-powered security analysis system developed by the startup depthfirst autonomously uncovered a critical vulnerability in NGINX that had remained hidden for 18 years
Key Vulnerability Details
Exposure Period: The vulnerability went undetected since its introduction in 2008, a span of 18 years.
Affected Versions: NGINX versions from 0.6.27 to 1.30.0.
Vulnerability Mechanism: The flaw resides in the rewrite module, stemming from a defect in the script engine's two-phase processing mechanism, which leads to a heap buffer overflow.
Patched Version: An official patch has been released. It is recommended to upgrade to the open-source version 1.31.0 or 1.30.1, or the corresponding commercial NGINX Plus release.
The Power of AI-Powered Security Analysis
This vulnerability was discovered by the San Francisco-based AI lab depthfirst. The system's capabilities have drawn significant industry attention:
High Efficiency: During just 6 hours of autonomous scanning, the system identified five security issues, including CVE-2026-42945 (four of which have been officially confirmed as remote memory corruption vulnerabilities).
Deep Comprehension: Unlike traditional tools, this AI understands complex business logic and cross-module interactions, uncovering vulnerabilities that even leading AI security tools had missed.
Data indicates approximately 19 million exposed NGINX instances are vulnerable. The United States (roughly 53.4 million affected instances, including historical data) and China (about 25.4 million) show the highest exposure levels. With the proof-of-concept (PoC) code now public, the security risk is severe. All enterprises and developers using NGINX are urged to immediately review their configuration files (particularly in scenarios using both rewrite and set directives) and complete version updates as soon as possible.








 DeepMind CEO Hassabis: I sleep six hours a day, usually feel energetic around 1 a.m.
Fortune recently featured an interview with Demis Hassabis, CEO of Google DeepMind, revealing his unconventional approach to rest and productivity. Hassabis disclosed that he sleeps very little, structuring his waking hours into two distinct work blo
 OpenAI, Anthropic Vie for Market Share Despite Revenue Shortfalls
Despite recent reports suggesting OpenAI missed revenue targets, creating pressure on tech stocks this Tuesday, private AI lab investors remain resilient. Seasoned backers have confirmed they will not reduce investment despite negative media coverage
California AV Compliance: A New Era of Tickets, Geofences, and 1M Miles
Guident operates an AuveTech shuttle in South Florida, managing a four-mile route in West Palm Beach and a one-mile route in Boca Raton using its remote monitoring technology. | Credit: GuidentCalifornia is redefining the regulatory landscape for dri

2026 Latest Best Top-rated AI Roleplay Chat Apps for Language Practice, Interview Prep, and Daily Fluency! XIX.AI curates a powerful game-changing collection that offers free vs paid comparison, real-world tests, and updated rankings weekly. These must-try tools help you boost writing skills, overcome fluency challenges, and improve communication efficiency across all daily scenarios. Explore now to discover your perfect tool for language growth!
10 tools
xix.ai

2026 Latest Best Top-rated AI Stem Separation Tools Curated for Remix Production, Sampling Prep, and Karaoke Masters. These powerful game-changing tools offer real-world tests to deliver precise audio isolation, boosting productivity significantly. XIX.AI provides a weekly updated free vs paid comparison guide to help you find the must-try solution that suits your needs. Explore now to unlock your AI edge.
8 tools
xix.ai

2026 Latest Best AI SQL Copilots Ranked Top-Rated! XIX.AI curates a powerful game-changing collection for weekly updated real-world tests. These must-try tools help you generate accurate revenue dashboards, analyze sales funnels, and track product metrics swiftly, boosting productivity massively. Explore now to Discover your perfect tool for data-driven decision making! 238 characters
9 tools
xix.ai

2026 Latest Best Top-Rated AI Melody Writing Tools for Song Drafts! XIX.AI has curated a highly powerful game-changing collection that goes through rigorous real-world tests to deliver the best writing experience. You can find detailed free vs paid comparisons, accurate rankings, and must-try options designed to help you create stunning song drafts effortlessly and boost your creative productivity significantly. Explore now to discover your perfect tool!
8 tools
xix.ai

2026 Latest Best Top-rated AI Conversation Trainer Tools for Interview Practice are here on XIX.AI! This curated collection features powerful, game-changing tools that go through rigorous real-world tests to deliver accurate feedback. You’ll find a free vs paid comparison and detailed rankings to help you choose the must-try option that boosts your confidence and skills. Explore now to Discover your perfect tool for interview success!
12 tools
xix.ai

2026 Latest Best Top-rated AI Style Transfer Tools for Creative Experiments! XIX.AI has curated a powerful, game-changing collection of must-try tools that deliver exceptional results through real-world tests and rigorous rankings. These top solutions help creatives boost productivity significantly by accelerating content creation and unlocking endless creative possibilities. Explore now to discover your perfect tool and start creating today!
9 tools
xix.ai

This is wild. An AI finding a bug that hid for 18 years? Makes you wonder what else is lurking in the code we trust. 😬












