


 Home
Another customer of struggling startup Delve hit by major security breach
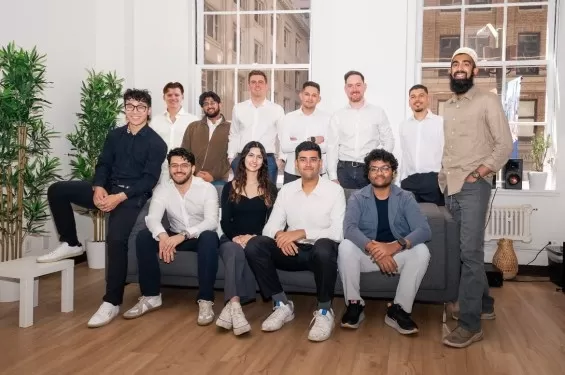
The compliance startup Delve continues to face a series of escalating controversies.
TechCrunch has verified that Delve conducted the security certifications for Context AI, an AI agent training firm that recently reported a security incident resulting in a data breach at the prominent app and website hosting platform Vercel.
Meanwhile, Lovable, which experienced its own security incident, is no longer using Delve’s services.
To recap: Last month, Delve faced intense scrutiny after an anonymous whistleblower claimed the startup fabricated customer data and utilized rubber-stamping auditors for its compliance certifications. Delve has denied these allegations.
Shortly thereafter, hackers targeted one of Delve’s security certification clients, LiteLLM, and injected malware into its open-source code. Following the breach, LiteLLM informed TechCrunch that it was terminating its relationship with Delve and seeking re-certification.
Delve also faced accusations of appropriating an open-source tool and presenting it as proprietary work without proper license attribution. The startup’s reputation deteriorated, leading Y Combinator, where Delve graduated, to sever ties.
Fast forward to last weekend, when Vercel announced that hackers had breached its internal systems and accessed certain customer data. The company stated that the breach occurred after an employee downloaded an application developed by Context AI and connected it to Vercel’s corporate account hosted on Google. The attackers exploited this employee’s access to their Google account to infiltrate parts of Vercel’s internal infrastructure.
Once Context AI was identified in connection with the Vercel attack, Gergely Orosz, author of the engineering newsletter The Pragmatic Engineer, posted on X that Delve had handled Context AI’s security certification.
Context AI has now confirmed to TechCrunch that it previously used Delve but has since discontinued the partnership and is currently undergoing re-certification.
“Yes, Context was previously a Delve customer,” a spokesperson for Context AI told TechCrunch. “Following the reporting surrounding Delve in March, we transitioned our compliance program to Vanta and engaged Insight Assurance, an independent audit firm, to conduct new examinations. As part of the re-examination, we began updating our public materials, and we’ll share the new attestation when it is complete,” the spokesperson added.
Security certifications alone do not prevent security incidents. Their purpose is to verify that a company has established policies and processes to mitigate attacks and reduce the risk of customer data compromise.
For example: Lovable was a Delve customer, but after the whistleblower’s allegations emerged, the vibe-coding platform stated it had terminated its relationship with Delve in late 2025. The company has already completed one security certification and is in the process of redoing others.
Nevertheless, Lovable admitted on Monday that it had inadvertently made customer chat data publicly accessible. The company also acknowledged dismissing vulnerability reports that had alerted it to the issue months earlier. Lovable apologized for initially denying a data breach, though it clarified that the problem stemmed from a configuration error rather than a hack.
Further strange developments are swirling around Delve. The anonymous whistleblower, known as DeepDelver, has published another post alleging that Delve was refusing refunds to customers while simultaneously taking its team of over 20 employees to an offsite meeting in Hawaii between April 15 and April 19.
The whistleblower provided compelling evidence to TechCrunch supporting the alleged Hawaii trip, but TechCrunch was unable to verify other claims.
Delve did not respond to requests for comment and confirmation, and an email sent to its media relations address bounced.
Related article
 Delve accused of deceiving customers with 'fake compliance' scheme
A recent anonymous Substack post accuses compliance startup Delve of misleading hundreds of customers into believing they were compliant with privacy and security regulations, potentially exposing them to criminal liability under HIPAA and substantia
Lovable strikes multi-year Google Cloud deal to boost usage 5x, source says
On Wednesday, Lovable and Google announced an expanded multi-year partnership. Lovable, the fast-growing Stockholm-based vibe-coding startup, has been a Google Cloud customer for some time. Under the new agreement, its usage will increase significant
Vercel CEO Guillermo Rauch hints at IPO as AI agents boost revenue
Unlike many startups founded before ChatGPT that now struggle to find their footing in the AI era, Vercel, a decade-old development tool and website hosting platform, is thriving due to the surge of AI-generated applications and autonomous agents.“Wh
Related Special Topic Recommendations
Academic Research
 Best AI Study Discovery Tools: Find Journals, Datasets, and Trends Quickly
2026 Latest Best Top-rated AI Study Discovery Tools are here on XIX.AI! This curated list includes powerful game-changing resources for quick access to journals, datasets, and industry trends. Get a free vs paid comparison along with real-world tests and updated rankings weekly. Must-try options help boost your research efficiency and unlock your AI edge. Explore now to discover your perfect tool!
 10 tools
 xix.ai
Marketing
AI Email Campaign Tools for Lifecycle Marketing
2026 Latest Best Top-Rated AI Email Campaign Tools for Lifecycle Marketing! XIX.AI has curated a powerful, game-changing collection of must-try solutions that boost writing efficiency, help create highly targeted content, and streamline entire marketing workflows. Enjoy weekly updated rankings, real-world tests, and a free vs paid comparison to find the perfect tool for your needs. Explore now to unlock your AI edge!
11 tools
xix.ai
Finance
Top AI Investment Research Tools: Compare Signals and Portfolio Risks
2026 Latest Top-Rated Best AI Investment Research Tools are here on XIX.AI! This curated list includes powerfully accurate signals to assess portfolio risks and help you make smarter, data-driven decisions. We conduct real-world tests weekly to update rankings and offer a free vs paid comparison. Discover your perfect tool to boost investment analysis efficiency today. Explore now!
10 tools
xix.ai
chatbot
AI Customer Chatbot Tools for Website Support
2026 Latest Best Top-Rated AI Customer Chatbot Tools for Website Support are here on XIX.AI! Our curated list features powerful, game-changing solutions that boost response speeds, improve customer satisfaction, and save tons of manual work. Each option goes through rigorous real-world tests, complete with free vs paid comparison details. Explore now to find the perfect tool that boosts your online support efficiency!
10 tools
xix.ai
Social Media
Instagram AI Comment Reply Tools for Shops, DMs, and Community Management
2026 Latest Best Instagram AI Comment Reply Tools for Shops, DMs, and Community Management! XIX.AI has curated a top-rated list of powerful game-changing solutions featuring weekly updated rankings, free vs paid comparison, and real-world tests. These must-try tools help boost productivity significantly by streamlining reply tasks, saving time, and enhancing customer engagement across all social media platforms. Explore now to discover your perfect tool for seamless community management!
10 tools
xix.ai
Image editing
Best AI Photo Retouch Tools for Portrait Editing
2026 Latest Best Top-Rated AI Photo Retouch Tools for Portrait Editing are here on XIX.AI! This curated list features powerful, game-changing solutions that help creators boost writing efficiency and unlock their full creative potential. We conduct real-world tests and provide detailed free vs paid comparison along with weekly updated rankings to ensure you find the must-try perfect tool for flawless portrait edits. Explore now to discover your ideal choice!
12 tools
xix.ai

 Comments (0)
0/500
The compliance startup Delve continues to face a series of escalating controversies.
TechCrunch has verified that Delve conducted the security certifications for Context AI, an AI agent training firm that recently reported a security incident resulting in a data breach at the prominent app and website hosting platform Vercel.
Meanwhile, Lovable, which experienced its own security incident, is no longer using Delve’s services.
To recap: Last month, Delve faced intense scrutiny after an anonymous whistleblower claimed the startup fabricated customer data and utilized rubber-stamping auditors for its compliance certifications. Delve has denied these allegations.
Shortly thereafter, hackers targeted one of Delve’s security certification clients, LiteLLM, and injected malware into its open-source code. Following the breach, LiteLLM informed TechCrunch that it was terminating its relationship with Delve and seeking re-certification.
Delve also faced accusations of appropriating an open-source tool and presenting it as proprietary work without proper license attribution. The startup’s reputation deteriorated, leading Y Combinator, where Delve graduated, to sever ties.
Fast forward to last weekend, when Vercel announced that hackers had breached its internal systems and accessed certain customer data. The company stated that the breach occurred after an employee downloaded an application developed by Context AI and connected it to Vercel’s corporate account hosted on Google. The attackers exploited this employee’s access to their Google account to infiltrate parts of Vercel’s internal infrastructure.
Once Context AI was identified in connection with the Vercel attack, Gergely Orosz, author of the engineering newsletter The Pragmatic Engineer, posted on X that Delve had handled Context AI’s security certification.
Context AI has now confirmed to TechCrunch that it previously used Delve but has since discontinued the partnership and is currently undergoing re-certification.
“Yes, Context was previously a Delve customer,” a spokesperson for Context AI told TechCrunch. “Following the reporting surrounding Delve in March, we transitioned our compliance program to Vanta and engaged Insight Assurance, an independent audit firm, to conduct new examinations. As part of the re-examination, we began updating our public materials, and we’ll share the new attestation when it is complete,” the spokesperson added.
Security certifications alone do not prevent security incidents. Their purpose is to verify that a company has established policies and processes to mitigate attacks and reduce the risk of customer data compromise.
For example: Lovable was a Delve customer, but after the whistleblower’s allegations emerged, the vibe-coding platform stated it had terminated its relationship with Delve in late 2025. The company has already completed one security certification and is in the process of redoing others.
Nevertheless, Lovable admitted on Monday that it had inadvertently made customer chat data publicly accessible. The company also acknowledged dismissing vulnerability reports that had alerted it to the issue months earlier. Lovable apologized for initially denying a data breach, though it clarified that the problem stemmed from a configuration error rather than a hack.
Further strange developments are swirling around Delve. The anonymous whistleblower, known as DeepDelver, has published another post alleging that Delve was refusing refunds to customers while simultaneously taking its team of over 20 employees to an offsite meeting in Hawaii between April 15 and April 19.
The whistleblower provided compelling evidence to TechCrunch supporting the alleged Hawaii trip, but TechCrunch was unable to verify other claims.
Delve did not respond to requests for comment and confirmation, and an email sent to its media relations address bounced.








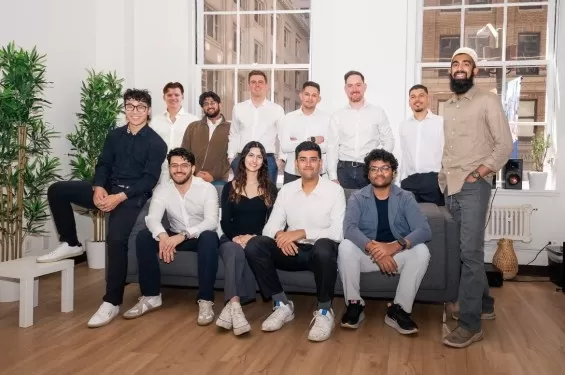 Delve accused of deceiving customers with 'fake compliance' scheme
A recent anonymous Substack post accuses compliance startup Delve of misleading hundreds of customers into believing they were compliant with privacy and security regulations, potentially exposing them to criminal liability under HIPAA and substantia
 Lovable strikes multi-year Google Cloud deal to boost usage 5x, source says
On Wednesday, Lovable and Google announced an expanded multi-year partnership. Lovable, the fast-growing Stockholm-based vibe-coding startup, has been a Google Cloud customer for some time. Under the new agreement, its usage will increase significant
 Vercel CEO Guillermo Rauch hints at IPO as AI agents boost revenue
Unlike many startups founded before ChatGPT that now struggle to find their footing in the AI era, Vercel, a decade-old development tool and website hosting platform, is thriving due to the surge of AI-generated applications and autonomous agents.“Wh
2026 Latest Best Top-rated AI Study Discovery Tools are here on XIX.AI! This curated list includes powerful game-changing resources for quick access to journals, datasets, and industry trends. Get a free vs paid comparison along with real-world tests and updated rankings weekly. Must-try options help boost your research efficiency and unlock your AI edge. Explore now to discover your perfect tool!
10 tools
xix.ai
2026 Latest Best Top-Rated AI Email Campaign Tools for Lifecycle Marketing! XIX.AI has curated a powerful, game-changing collection of must-try solutions that boost writing efficiency, help create highly targeted content, and streamline entire marketing workflows. Enjoy weekly updated rankings, real-world tests, and a free vs paid comparison to find the perfect tool for your needs. Explore now to unlock your AI edge!
11 tools
xix.ai
2026 Latest Top-Rated Best AI Investment Research Tools are here on XIX.AI! This curated list includes powerfully accurate signals to assess portfolio risks and help you make smarter, data-driven decisions. We conduct real-world tests weekly to update rankings and offer a free vs paid comparison. Discover your perfect tool to boost investment analysis efficiency today. Explore now!
10 tools
xix.ai
2026 Latest Best Top-Rated AI Customer Chatbot Tools for Website Support are here on XIX.AI! Our curated list features powerful, game-changing solutions that boost response speeds, improve customer satisfaction, and save tons of manual work. Each option goes through rigorous real-world tests, complete with free vs paid comparison details. Explore now to find the perfect tool that boosts your online support efficiency!
10 tools
xix.ai
2026 Latest Best Instagram AI Comment Reply Tools for Shops, DMs, and Community Management! XIX.AI has curated a top-rated list of powerful game-changing solutions featuring weekly updated rankings, free vs paid comparison, and real-world tests. These must-try tools help boost productivity significantly by streamlining reply tasks, saving time, and enhancing customer engagement across all social media platforms. Explore now to discover your perfect tool for seamless community management!
10 tools
xix.ai
2026 Latest Best Top-Rated AI Photo Retouch Tools for Portrait Editing are here on XIX.AI! This curated list features powerful, game-changing solutions that help creators boost writing efficiency and unlock their full creative potential. We conduct real-world tests and provide detailed free vs paid comparison along with weekly updated rankings to ensure you find the must-try perfect tool for flawless portrait edits. Explore now to discover your ideal choice!
12 tools
xix.ai












